01
AWS Architecture Review & Solution Design
Get an architecture you can defend before you spend on implementation or expand what you already run.
- ▸ Current-state review
- ▸ Target architecture diagram
- ▸ Prioritised roadmap
Cloud Architect · AWS Cloud Security & Automation
I help growing businesses and IT teams design, migrate, secure and automate AWS — with clear plans, agreed scope and documentation you keep.
Evidence: designed and operated AWS environments supporting 50+ production applications across 15+ client accounts; reduced over-privileged access by over 60% through IAM standardisation.
Sound familiar?
Growth is straining your applications
Slowdowns and outages appear as customers increase.
→ Architecture review
You need to migrate without disruption
Unknown dependencies make every cutover risky.
→ Migration planning
Too many people have too much access
Shared admin logins and old keys widen the impact of any mistake.
→ Security assessment
The AWS bill keeps rising
Nobody can say which team or resource is responsible.
→ Cost review
Deployments are manual
Releases are slow, inconsistent and depend on one person.
→ Automation
Backups have never been tested
You can't say how much data you would lose.
→ Monitoring & recovery
No in-house AWS expertise
Questions and changes wait, or happen without review.
→ Ongoing support
Services
Decide what to build and move it safely. For businesses planning AWS, outgrowing their current setup, or moving workloads without disrupting customers.
01
Get an architecture you can defend before you spend on implementation or expand what you already run.
02
Move suitable applications, websites or infrastructure to AWS with a tested cutover and a way back.
See your risks and fix what matters first. For businesses unsure who has access to what, whether logs exist, or how exposed their workloads are.
03
Find access, configuration and visibility gaps — then fix them in a sensible order.
04
An organised, secure starting point for AWS — sized to your business, not to a textbook.
Run AWS reliably, repeatably and affordably. For businesses with manual deployments, untested backups, unexplained bills or no one to call.
05
Know when things fail, and know — because you tested it — that you can restore.
06
Replace repetitive manual changes with version-controlled infrastructure and reliable pipelines.
07
Understand your AWS bill, see where money goes, and prioritise sensible savings.
08
Continuing AWS help under clearly defined hours, channels and responsibilities.
Ways to engage
Assessment
Understand the current situation and receive prioritised recommendations.
Best when you're unsure what's wrong, or need evidence before spending.
Implementation Project
Deliver an agreed architecture, migration, security or automation scope.
Best when you know what's needed and want it built and documented.
Ongoing Support
Continuing help under defined responsibilities, hours and coverage.
Best when you lack in-house AWS expertise or want regular reviews.
Why work with me
Grounded in implementation
I've designed and operated production AWS environments supporting 50+ live applications across 15+ client accounts.
Security considered during design
Least-privilege access, encryption and logging are part of the first design.
Practical scope
Right-sized recommendations — no complex landing zone where three accounts will do.
Clear documentation
Every engagement ends with handover material your team can use.
Ongoing costs in view
Designs account for the AWS bill and the effort to operate them.
Direct communication
No account managers in between — you talk to the person doing the work.
Evidence
Production client work
Problem: SMEs, schools and microfinance clients needed dependable hosting without running their own infrastructure teams.
My role: AWS Cloud Architect — designed and operated the environment.
Built: Multi-tenant environment on EC2, VPC, RDS, S3 and IAM, supporting live applications across many client accounts.
Result: Supported 50+ live production applications across 15+ client accounts.
Production client work
Problem: Inconsistent access patterns had left users and services with more permissions than they needed.
My role: Designed and rolled out the access model.
Built: Role hierarchies, enforced MFA and quarterly access audits across client accounts.
Result: Over-privileged access reduced by over 60%.
Production client work
Problem: Clients' AWS bills had grown without clear accountability.
My role: Led the review and recommendations.
Built: Usage analysis, rightsizing and storage changes matched to workload needs.
Result: 20–25% AWS cost reductions for three clients without degrading SLAs.
Production client work
Problem: Repeated manual builds for client environments were slow and inconsistent.
My role: Built the modules and advised on migration strategy for 10+ clients.
Built: Reusable infrastructure-as-code modules for client environments.
Result: Repeatable, documented environment builds used across client work.
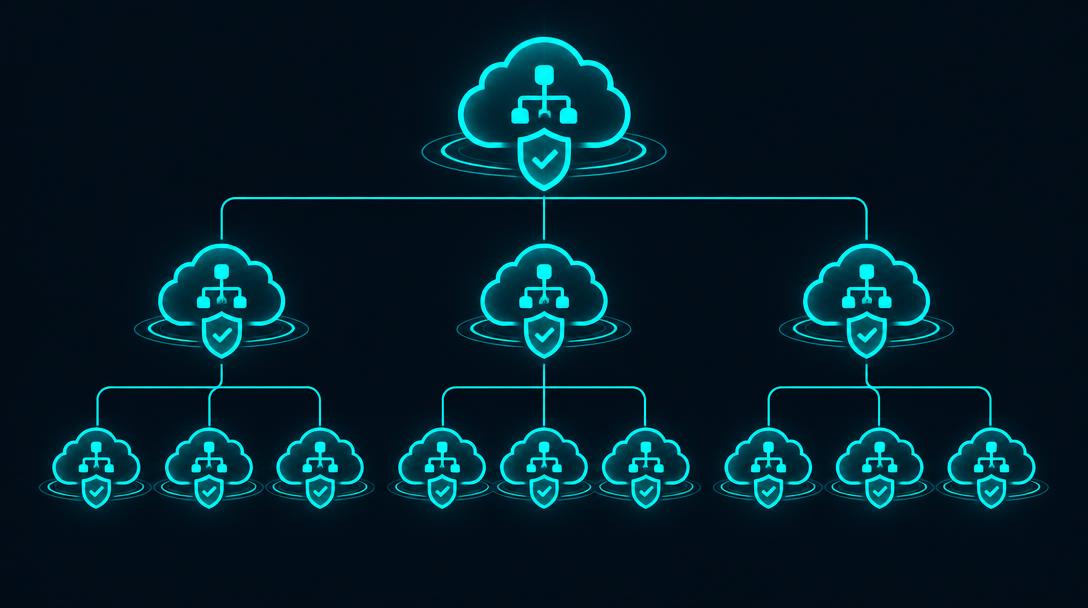
Architecture portfolio project
Problem: A growing multi-account AWS estate needs consistent guardrails and central visibility without slowing delivery teams.
My role: Reference architecture — not a client deployment.
Built: AWS Organizations, Control Tower, SCPs, Config, CloudTrail, Security Hub and GuardDuty.
Result: Documented reference design available on GitHub.
View on GitHub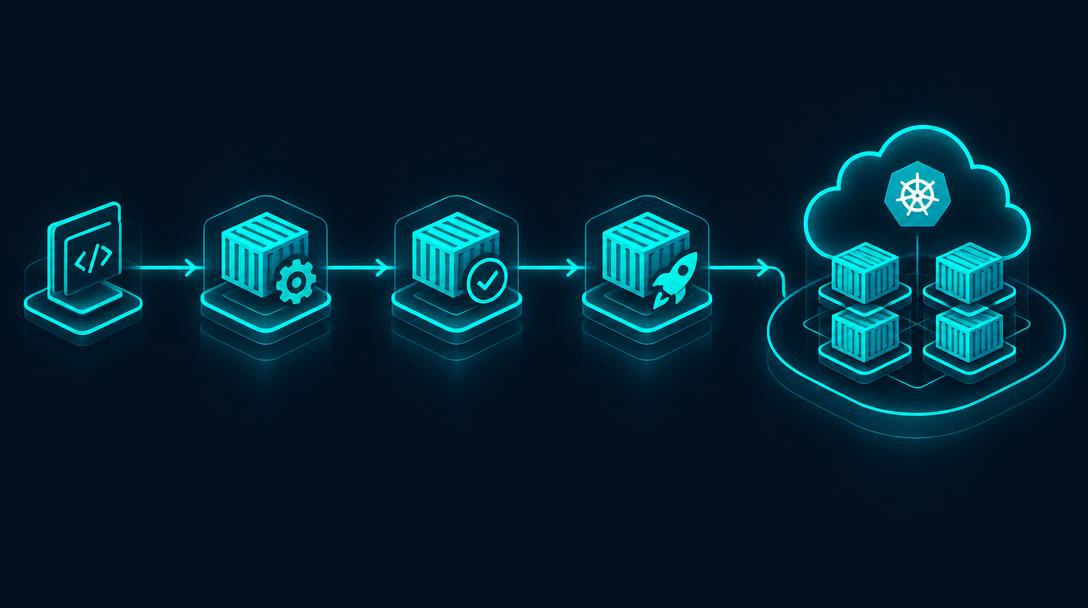
Architecture portfolio project
Problem: Manual releases create delays and inconsistent environments.
My role: Reference architecture — implementation awareness.
Built: Docker → ECR → CodePipeline / GitHub Actions → Terraform / CloudFormation.
Result: Documented reference pipeline available on GitHub.
View on GitHubCredentials
Aspiring to the AWS Golden Jacket—building practical expertise across cloud architecture, security, networking, automation and operations. This is a personal learning goal, not an earned credential. I am an independent consultant and not an AWS Partner; nothing here implies AWS endorsement.
How it works
01
Discovery
Short call to understand the problem.
02
Assessment
Review what exists, with your access approval.
03
Proposal
Written scope, deliverables and fee.
04
Implementation
Agreed work, with your approvals.
05
Validation
Check results against agreed criteria.
06
Handover
Documentation and walk-through.
Estimate
| Service | Effort | One-off | Monthly | |
|---|---|---|---|---|
| AWS Architecture Review & Solution Design | 23.5h | $2,233 | — | |
| AWS Migration Planning & Implementation | 46h | $4,370 | — | |
| AWS Security Assessment & Hardening | 18h | $1,710 | — | |
| Secure AWS Foundation & Landing Zone | 37h | $3,515 | — | |
| AWS Monitoring, Backup & Recovery Setup | 26h | $2,470 | — | |
| AWS Infrastructure & Deployment Automation | 43h | $4,085 | — | |
| AWS Cost Review & Optimisation | 22h | $2,090 | — | |
| Ongoing AWS Advisory & Operational Support | 4h + 11h/mo | $760 | $935/mo |
Illustrative estimate — rates pending confirmation. Each row is independent; USD, taxes excluded, AWS usage billed separately.
FAQ
Yes. I use a temporary, read-only role that you create and control, and you receive written findings.
Yes. Most engagements involve your team, with pairing and documentation so they can own the result.
Yes — an architecture review or right-sized foundation is a good first step before building anything.
Some workloads need a short cutover window. Acceptable downtime is agreed per workload after assessment, with a rehearsal and rollback path.
You do. Accounts, code and documentation stay with you. I work through approved roles and temporary credentials — never root credentials.
No. AWS bills usage directly to your account. My fee covers professional services only.
A short description of the problem, the workloads and accounts involved, and any deadlines or constraints. The calculators help you outline this.
Yes. An assessment gives you prioritised recommendations, and you decide afterwards whether to proceed.
You receive handover documentation and a walk-through. Ongoing support is optional.
Yes, under agreed monthly hours, channels and responsibilities. Availability, response times and coverage are agreed during scoping — there is no implied 24/7 cover.
Next step
Scope, timelines and any availability or support commitments are agreed in writing before work begins.